██████╗ ██████╗ ███╗   ███╗
██╔═══██╗██╔══██╗████╗ ████║
██║   ██║██████╔╝██╔████╔██║
██║   ██║██╔═══╝ ██║╚██╔╝██║
╚██████╔╝██║     ██║ ╚═╝ ██║
 ╚═════╝ ╚═╝     ╚═╝     ╚═╝
On-chain
Package Security
Cryptographic attestation via ECDSA-signed manifests, multi-model AI auditing through intelligence-weighted LLM consensus, and immutable risk scoring anchored to Base L2. Zero-knowledge agent verification. Tamper-evident by design.
Every command, security-first.
Drop-in replacement for npm. Every operation gains cryptographic verification, AI-powered auditing, and on-chain attestation transparently.
Push
ECDSA-sign package manifest, dispatch to 3 independent LLM agents for parallel static analysis, aggregate weighted risk scores, register immutable attestation on Base L2
Install
Resolve ENS identity, verify ECDSA signature against on-chain registry, validate SHA-256 checksum, cross-reference OSV CVE database before extraction
Check
Traverse full dependency DAG, run Levenshtein-distance typosquat detection against top 10k packages, OSV CVE lookup, upload report to Fileverse (IPFS)
This is happening
right now.
Supply chain attacks on npm aren't theoretical. Developers are losing money, shipping CVEs, and installing malware — every single week.
6,847
Malicious packages
removed from npm in 2025
$15M+
Developer losses
from wallet drainer packages
23%
Projects affected
by known CVEs in deps
4 hrs
Avg time to detect
a supply chain attack
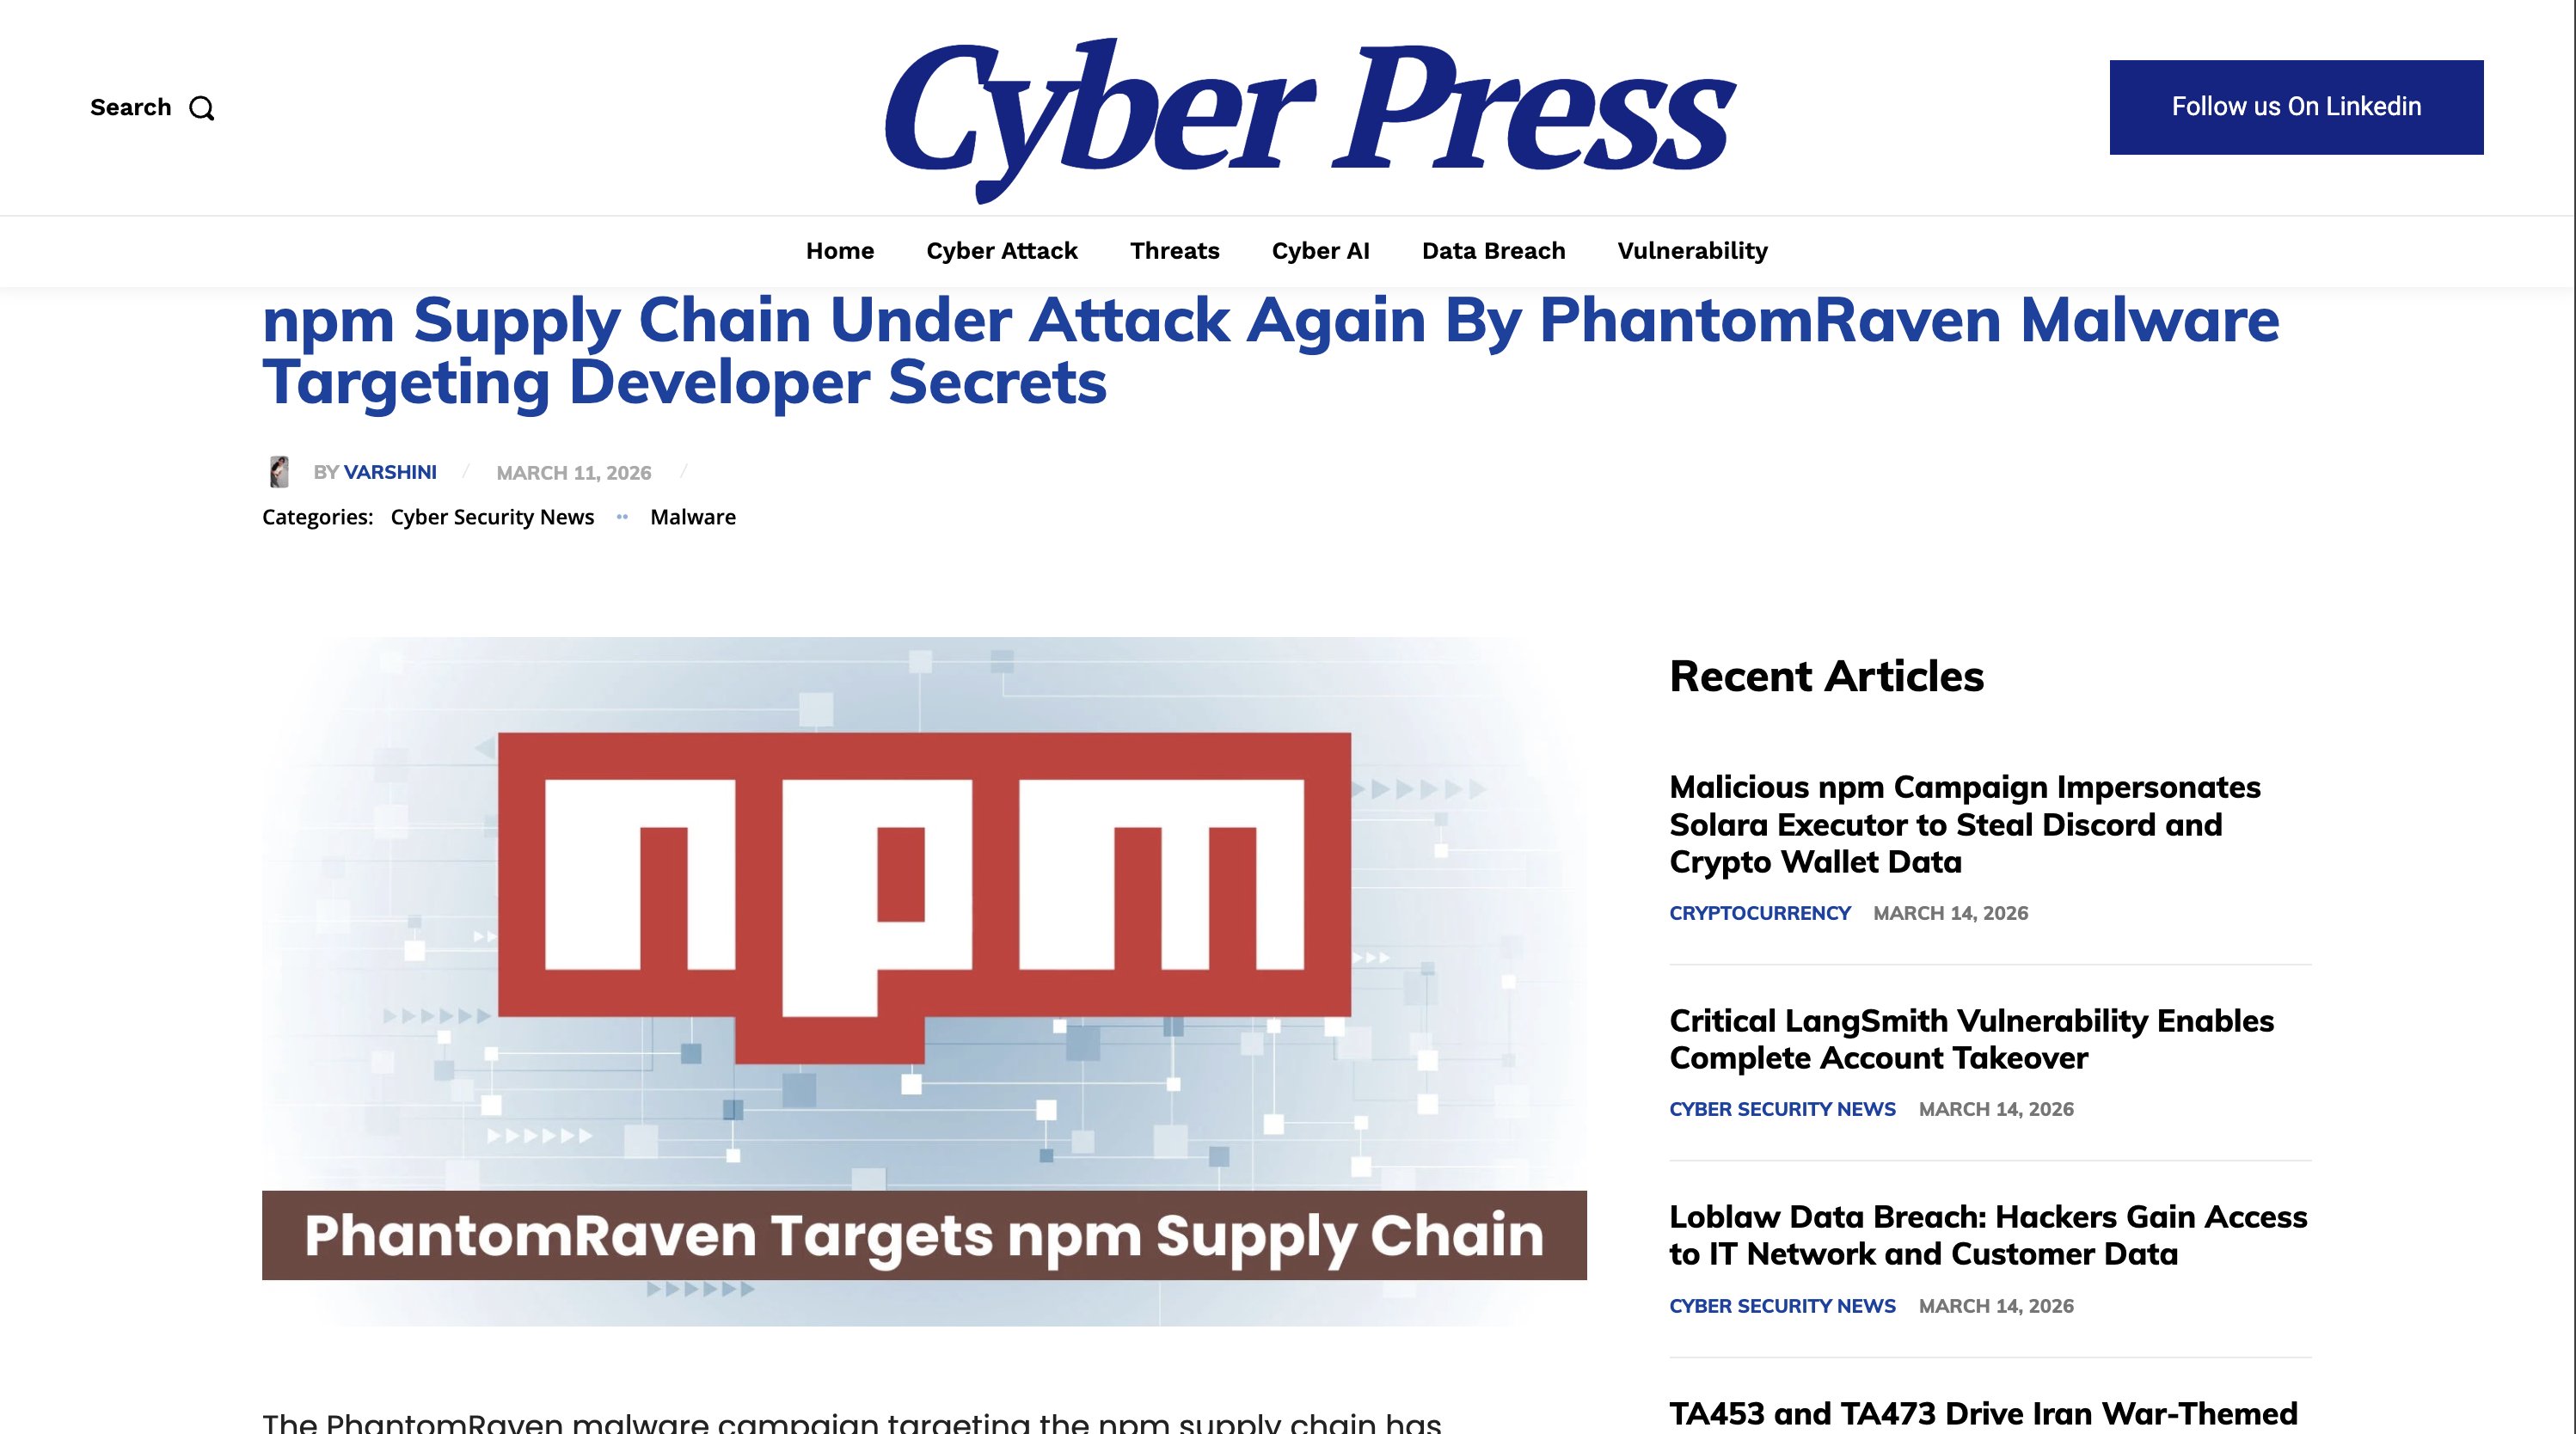
PhantomRaven Targets npm Supply Chain
Malware campaign targeting developer secrets through typosquatted packages. Thousands of downloads before detection.
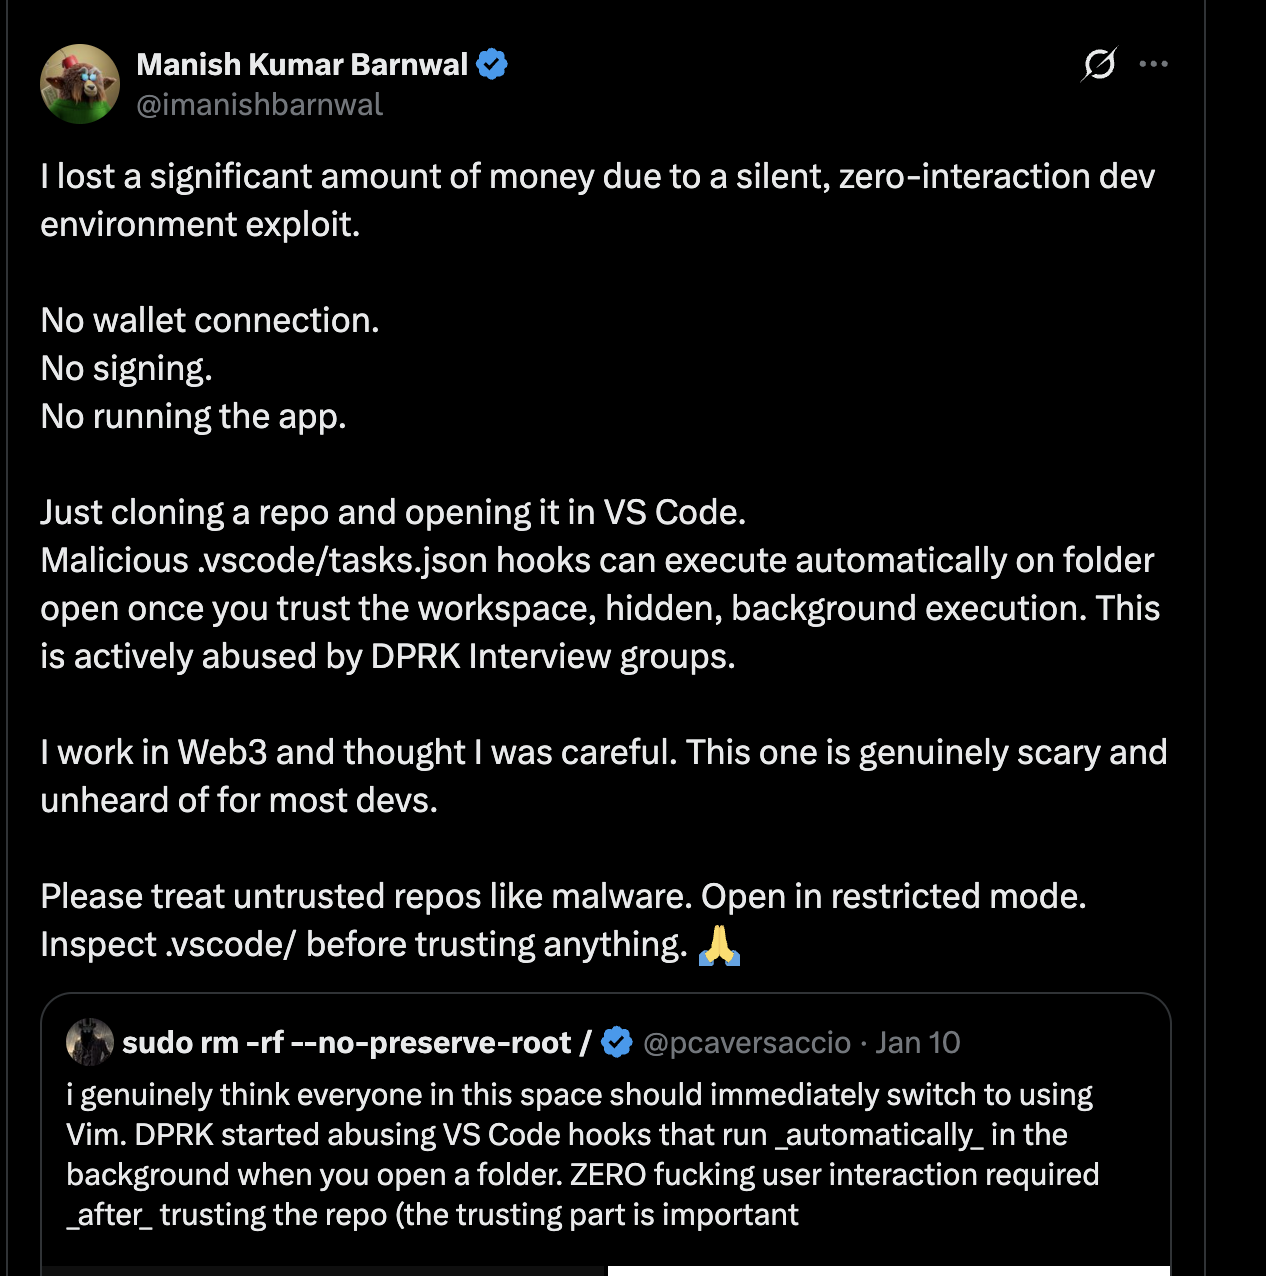
“I lost a significant amount of money due to a silent, zero-interaction dev environment exploit.”
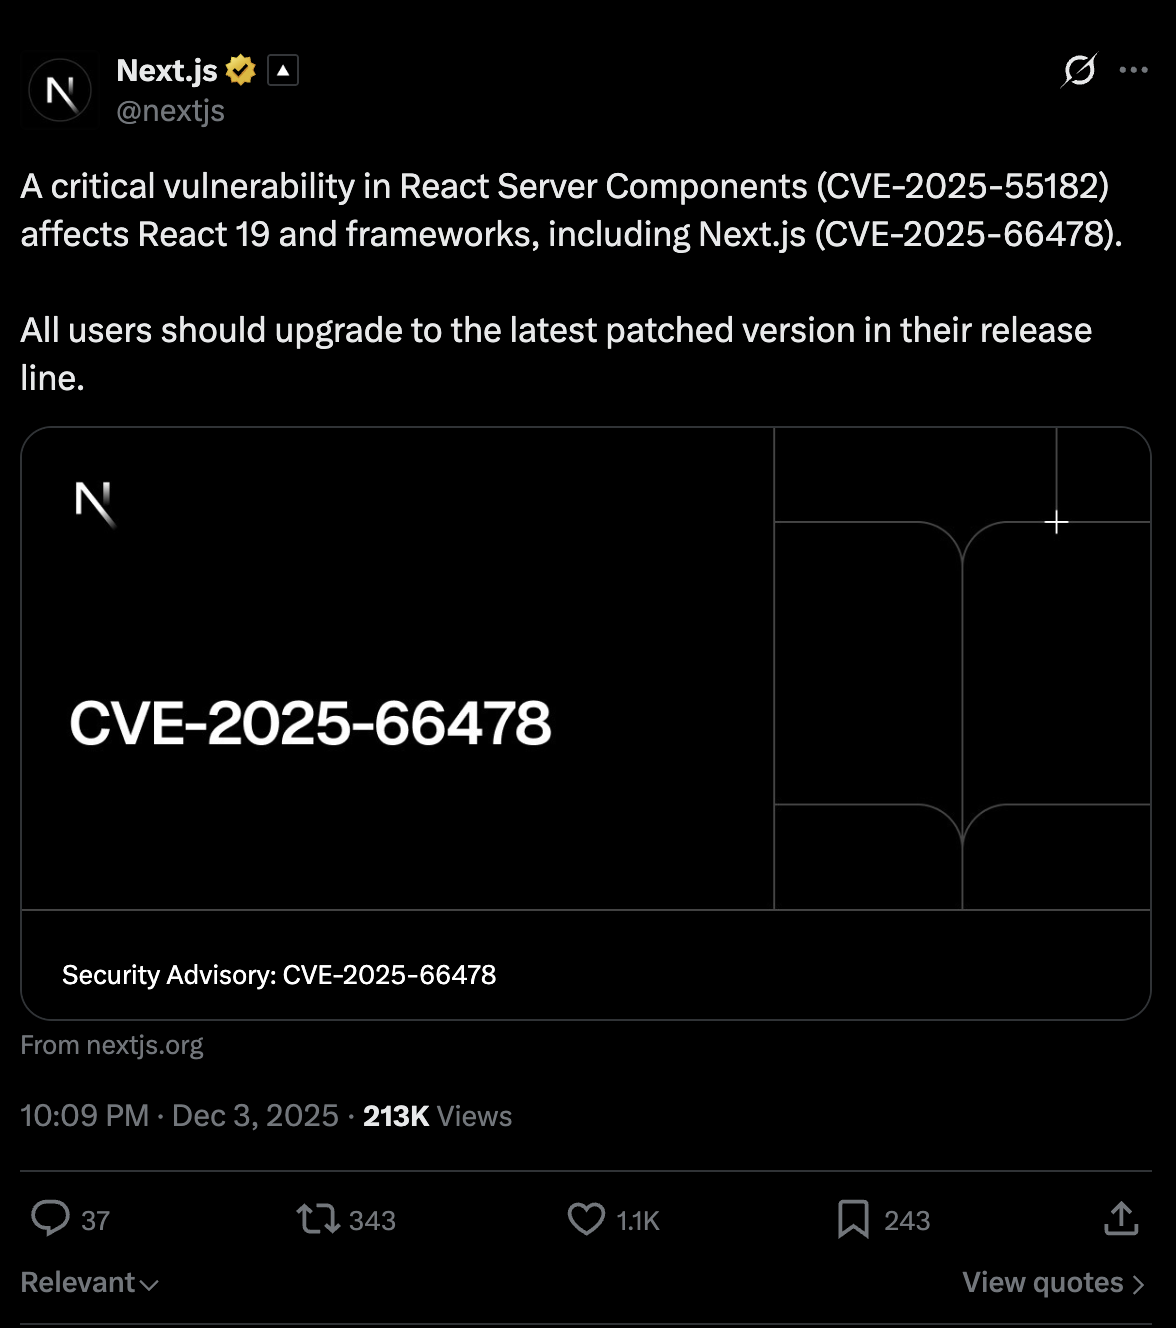
Critical vulnerability in React Server Components affecting Next.js. 213K+ views.
How developers react to yet another critical CVE in their dependency tree.
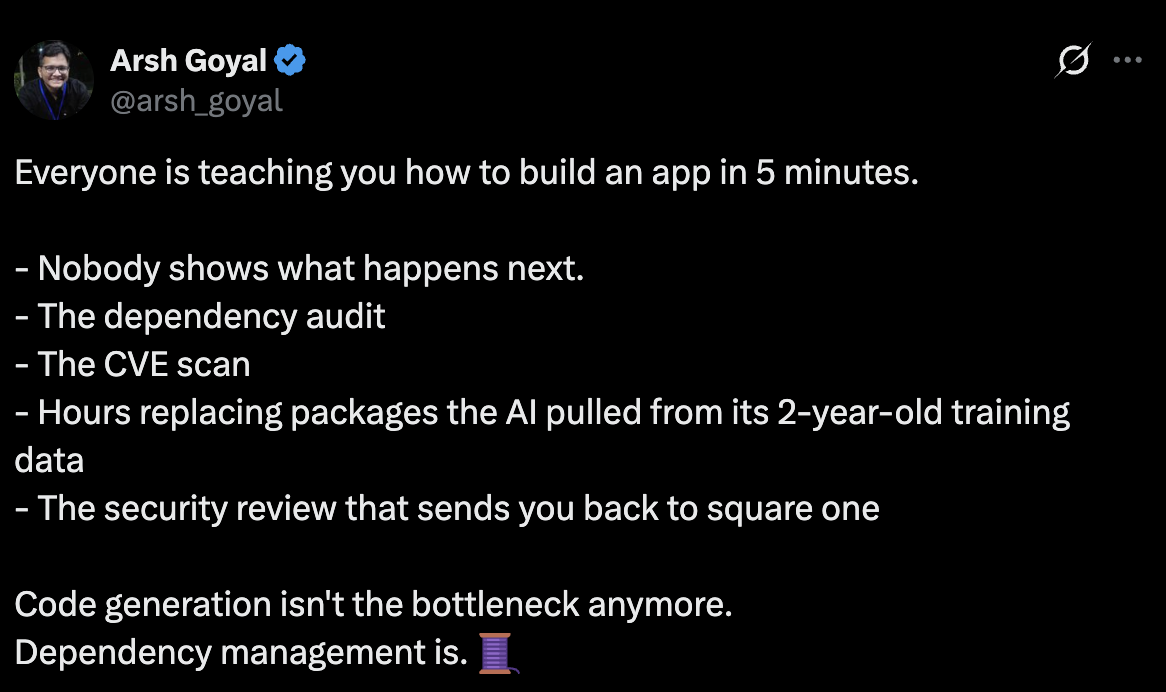
“Code generation isn't the bottleneck anymore. Dependency management is.”
OPM catches these before they reach your node_modules.
Security Primitives
Defense in depth, by default.
Multi-Agent Consensus
N-of-M heterogeneous LLM ensemble with intelligence-weighted scoring derived from live Artificial Analysis quality and coding indices. Byzantine fault-tolerant by design.
Verification Pipeline
Five-stage cryptographic attestation pipeline: from ECDSA signing through multi-agent consensus to on-chain settlement. Every package is verified before extraction to node_modules.
Pack & Sign
SHA-256 content-addressable checksum + secp256k1 ECDSA signature via author wallet
Multi-Agent Scan
Parallel dispatch to N heterogeneous LLMs; each submits independent risk vector
Weighted Consensus
Intelligence-weighted aggregate via Artificial Analysis quality + coding indices
On-chain Registry
Package metadata, agent scores, Fileverse report URI settled on Base Sepolia L2
Install Verify
ECDSA signature + on-chain score lookup + OSV CVE cross-reference at extraction time
Fully on-chain. Fully verifiable.
OPMRegistry.sol deployed on Base Sepolia L2. Every package registration, agent score submission, ZK-verified agent authorization, and ENS-resolved author profile is an immutable on-chain record. Fully queryable, fully verifiable.
Registered
Packages
Submitted
Agent Scores
Verified
Authors
On IPFS
Reports